Showing posts with label IIS. Show all posts

How to block external access to the Exchange Admin Center

Tuesday, October 2, 2018


When I was at Microsoft Ignite last week, several customers asked me how to block external access to the Exchange Admin Center. These customers have already completed all their mailbox migrations to Exchange Online and understand they'll need to keep that last Exchange server on-prem as a management server to manage mailboxes, groups, contacts, etc. But now that everyone in their organization has been migrated to Exchange Online, there's no need to allow external access to the hybrid servers for OWA or ECP.

There are several ways to do this:

  1. Remove the OWA/ECP namespace from external DNS so external clients can't resolve the FQDN
  2. Disable external EAC access on all ECP virtual directories using the following cmdlet (thanks to @markes20754 for reminding me) :
    Get-EcpVirtualDirectory | Set-EcpVirtualDirectory -AdminEnabled $false
Note that the command above will disable EAC on all Exchange servers, both internally and externally. You'll need another internal server for administration.

The third way is to limit access to only internal IP addresses using IIS, as shown below:
  • Start by adding the IP Address and Domain Restrictions feature to the Web Server (IIS) role in Server Manager for each Exchange 2013/2016 hybrid server in the org. This does not require a restart.
  • Open Internet Information Services (IIS) Manager and expand Default Web Site to the ECP virtual directory.
  • Double-click IP Address and Domain Restrictions and click Add Allow Entry on the Actions pane and enter the range for your internal LAN. In the following example I've configured the 192.168.1.0/24 LAN network.
    • Optionally, you can add other public IP address(es) that you want to allow access from.
    • Click Edit feature settings on the Actions pane. Under Access for unspecified clients select Deny and select the type of error message users see in their browser when they are denied. In the example below, I selected Abort.
    • Enable Proxy Mode allows IP addresses to be blocked not only by the client IP that is seen by IIS, but also by the values that are received in the x-forwarded-for HTTP header. Enable this option if SNAT is enabled on your load balancer.
    • Repeat for the OWA virtual directory.
    • Repeat the steps above for each Exchange hybrid server.
    Now if the Exchange Admin Center is accessed externally users will get an error:


    Notes:
    1. This change goes into effect immediately. There’s no need to restart IIS.
    2. Only do this after all your user mailboxes have been migrated to Exchange Online since doing this will prevent users with mailboxes on-prem from using OWA and will break free/busy sharing coexistence with on-prem users.
    3. Exchange 2019 does not publish the Exchange Admin Center externally by default. You need to manually configure it to do so. See Exchange admin center in Exchange Server 2019 for more details.

    Read more ...

    How to Perform HTTP -> HTTPS Redirection in a Single Exchange Server Environment

    Tuesday, August 30, 2016
    HTTP to HTTPS redirection in Outlook Web App is a user convenience that many admins consider a necessity. It automatically redirects the user's browser to https://mail.contoso.com/owa if they enter http://mail.contoso.com, or simply mail.contoso.com. Without redirection, the user will get an HTTP 403 Forbidden error page, like the one below.


    This happens because the SSL settings on the Default Web Site and all subdirectories are configured to require SSL.

    In multi-server environments where load balancers are used, HTTP -> HTTPS redirection is normally performed on the load balancer. Most load balancers, such as KEMP or F5, automatically configure it when you deploy one of their Exchange server templates.


    In single Exchange environments without a load balancer, you must configure redirection directly on the server itself. The steps below explain how to do this. I've used this method since Exchange 2007 and it works perfectly 100% of the time. Other methods I've seen on the Internet sometimes cause routing errors.

    • Open Internet Information Services (IIS) Manager on the Exchange 2016 or Exchange client access server and navigate to Sites > Default Web Site.
    • Double-click Error Pages and add a new custom error page for status code 403.4 that responds with a 302 redirect to https://mail.contoso.com/owa.


    • Special note for Exchange 2016 - The Exchange team did a little number in the web.config file on Exchange servers to "improve performance", but it removes the custom error page behavior. So you'll need to do the following:
      • Open the C:\inetpub\wwwroot\web.config file in Notepad.
      • Remove the following line, and then save and close Notepad:
    <remove name="CustomErrorModule" />


    Note that this web.config edit will need to be made after every Exchange 2016 CU installation since setup overwrites this file.

    That will handle the HTTP 403.4 - Forbidden: SSL is required error behavior in the browser. All that's left is to handle what happens when a user enters https://mail.contoso.com.

    • Using Notepad, create a web page called default.htm in the C:\inetpub\wwwroot folder of the Exchange 2016 or client access server. Add the following three lines:

    <html>
    <meta http-equiv="REFRESH" content="0;url=/owa">
    </html>
    • Save and close Notepad, and then test redirection.

    Read more ...

    Redirection in Exchange 2013 CU6+ and Exchange 2016

    Monday, May 2, 2016

    Beginning with Exchange 2013 Cumulative Update 6, the Exchange 2013/2016 application itself performs redirection from the default website to the /OWA virtual directory. That means that if a user goes to https://server.contoso.com Exchange will redirect the user's browser to https://server.contoso.com/owa.

    This 301 redirect behavior may affect load balancer health checks if your load balancer does not support direct URL health checking. Application-level health checks should normally be made directly to the https://server.contoso.com/<protocol>/healthcheck.htm URL. Citrix NetScaler load balancers, for example, perform healthchecks by connecting first to the default website and then performing a GET /OWA command. Since Exchange 2013 CU6 and later redirect the client (the load balancer) to the /OWA virtual directory this breaks that functionality.

    The only reference to this new behavior is in the support article, Load balancer marks Exchange server as down in an Exchange Server 2013 Cumulative Update 6 environment. At the time of this writing, the article says this behavior applies to Microsoft Exchange Server 2013 Standard and Enterprise and that, "Microsoft has confirmed that this is a problem in the Microsoft products that are listed in the 'Applies to' section." I have confirmed with the product team that this is by design, not a problem. It also applies to all versions of Exchange 2016 Standard and Enterprise, as well. Microsoft will be updating the support article soon to reflect this.

    Note that this behavior does not redirect HTTP requests to HTTPS. You still need to perform these redirects from the server or the load balancer. My preference is to do this from the server(s).

    Here's how I recommend implementing HTTP -> HTTPS redirection on Exchange Servers:

    • Open Internet Information Services (IIS) Manager on the Exchange Server and select the server name.
    • Double-click Error Pages.
    • Click the Add action on the right and create a new error page for status code 403.4 that responds with a 302 redirect to https://server.contoso.com/owa as shown below.


    Since the default website on Exchange servers is configured to require SSL, a user who tries to connect via HTTP will then get redirected to https://mail.contoso.com/owa, rather than getting an error page saying, "HTTP 403 Forbidden" and that SSL is required or you are required to log in.

    With Exchange 2013 CU6 or later that's all you need to do. With older versions of Exchange you should create a default.htm file in the C:\inetpub\wwwroot folder with the following:
    <html>
    <meta http-equiv="REFRESH" content="0;url=/owa">
    </html>
    This will cause anyone who connects to https://mail.contoso.com to be redirected to https://mail.contoso.com/owa, which is now the default behavior with Exchange 2013 CU6 or later.

    Read more ...

    Chrome Browser Now Warns About Weak SHA-1 Certificates

    Monday, December 14, 2015
    *** ACTION REQUIRED ***

    The Google Chrome web browser is now warning users if Outlook on the web (OWA) or other websites are using SHA-1 SSL certificates.

    These certificates are no longer considered secure and should be replaced ASAP. Please read my article, "Is Your Organization Using SHA-1 SSL Certificates?" on Windows IT Pro for more information and steps you should take.

    SHA1 certificates are being sunsetted by January 1, 2017. These certs should be replaced or re-keyed with SHA256 certs to improve security and prevent outages.
    Read more ...

    Is Your Organization Using SHA-1 SSL Certificates?

    Tuesday, November 11, 2014

    I just published an article on Windows IT Pro about Microsoft's decision to block Windows from accepting SHA-1 SSL certificates. This has important ramifications for your users and your IT environment. Don't be caught unaware.

    Read "Is Your Organization Using SHA-1 SSL Certificates?" on Windows IT Pro here.

    Read more ...

    How to Configure an Internal SMTP Relay Server for Office 365

    Saturday, October 26, 2013
    Most organizations have internal application servers and appliances that send emails to users or groups. Examples include copier/scanners and application servers, such as backup servers that notify admins of a completed or failed backup job.

    If the organization has Exchange on-prem you would normally configure an internal relay receive connector in Exchange and configure the internal resources to send emails to Exchange. But what do you do when you've migrated all your mailboxes to Office 365 and have decommissioned your Exchange servers?

    The solution is to install an IIS SMTP relay server in your internal network, configure it to accept email from specific IP addresses, and forward emails to Office 365. You can also configure the SMTP relay for external domains, if necessary.

    Here's how to do it:
    • Install the SMTP Server feature and its dependencies to a new or existing Windows server. This will be your relay server and your firewall needs to allow it to send SMTP traffic (TCP port 25) outbound to the Internet. I typically use the DirSync server, if there is one.
    Adding the SMTP Server feature and its dependencies to Windows Server 2012
    • Open Internet Information Services (IIS) 6.0 Manager to configure the SMTP relay.
    • Configure the properties of [SMTP Virtual Server #1] as follows:
      • On the Access tab:
        • Authentication: Only Anonymous access is checked.
        • Relay: Only the list below. Add IP addresses or ranges of servers allowed to relay.
        • Note - It's important to only allow IP addresses you trust to relay through this server. Any IP address you enter here will be allowed to send emails on behalf of your domain.
      • On the Messages tab:
        • Adjust message size limits. The default message size limit is 2048 KB (2 MB).  You may want to change it to 10240 KB (10 MB) or more to allow for larger messages from copier/scanners, etc.
      • On the Delivery Tab:
        • Outbound Security: Anonymous access only and no TLS encryption.
        • Outbound Connections: Port 25
        • Advanced: Leave the Smart Host field blank
    • Add new remote domains:
      • Right-click Domains > New > Domain and add the domain(s) hosted in Exchange Online.
      • If the relay server is allowed to relay emails to other external domains add a new *.com remote domain. Repeat for *.org, *.net, etc. as necessary.
      Add Office 365 and other remote domains if required for external relay
      • For properties of each domain hosted in Exchange Online:
        • Use www.mxtoolbox.com to get the EOP endpoint (MX record) for your tenant. For example, contoso-com.mail.protection.outlook.com.
        • Check Allow incoming mail to be relayed to this domain
        • Forward all mail to this smart host: The EOP endpoint you identified above (i.e., contoso-com.mail.protection.outlook.com)
        • Outbound Security: Check Anonymous access and TLS encryption
      • For properties of all other remote domains (if any):
        • Check Allow incoming mail to be relayed to this domain
        • Outbound Security: Check Anonymous access and do not check TLS encryption.
    • Restart IIS.  Be aware that whenever you restart IIS, the SMTP virtual server usually stays stopped – start it.

    Now we need to configure Exchange Online to accept emails from the new relay server. Recent changes in EOP email security require that you verify the relay server by specifying the SSL certificate or public IP address used by the relay server.
    • Sign-in to the Exchange Online Admin Center with your admin account
    • Navigate to Mail Flow > Connectors and add a new connector
    • On Select your mail flow scenario, select:
      • From: Your organization's email server
      • To: Office 365
    • Name the new connector "Relay from On-Premises" and click Next
    • On How should Office 365 identify email from your email server? you have two choices:
      1. If you have installed a valid third-party SSL certificate from a trusted CA on your SMTP relay server you can enter the Subject Name for the cert (i.e., mail.contoso.com, or *.contoso.com for a wildcard cert) on the new connector.
      2. If your SMTP relay server has a static public IP address you can enter that IP address. You can use a service like https://www.whatismyip.com/ to get your current IP address. Note that if this IP address ever changes, you'll need to update the connector in Exchange Online.
    • Confirm the new connector's setting and click Save.
    • Note that it can take up to 15 minutes for this connector and settings to propagate throughout EOP.


    Notes/Troubleshooting:
    • The SMTP Server feature can be added to any Windows 2003 or better server. I usually use the DirSync server if there is one.
    • Unlike Exchange, TLS for IIS 6 SMTP servers is not opportunistic. If the virtual server or a remote domain is configured to use TLS, email will not be sent if the remote domain does not support TLS. Office 365 offers TLS, so we can use it.
    • The configuration above allows the IIS 6 SMTP server to send emails to the Internet for the remote domains configured, so you should add the public NAT IP address for this server to your existing SPF record to prevent non-delivery. Use http://whatismyip.com from the SMTP server to determine the NAT IP address.
    • Monitor the %systemdrive%\Inetpub\mailroot\Queue folder to ensure that emails are being delivered.
      • If emails are not being delivered to Office 365 users, test sending email via Telnet. The IP address may be blocked by an Exchange Online Protection (EOP) blocklist and you will see that response from EOP. If so, send a delist request from your Office 365 admin account to delist@messaging.microsoft.com letting them know the IP address that should be delisted. In my experience it takes up to 36 hours for Microsoft to delist it.
      • If emails are not being delivered to external domains, ensure that you have a remote domain type (*.com, *.eu, etc.) configured for those email addresses.
    • You can enable logging in the properties of the SMTP virtual server for further troubleshooting. Use the NCSA Common Log File Format. IIS does not automatically groom or delete logs like Exchange does, so turn logging off when you're done troubleshooting.
    • The best practice is to create an A record in internal DNS for smtp.yourdomain.com using the SMTP relay server's IP, and configure all application servers and appliances to use that FQDN for email forwarding. That makes it easier to update in the future.


    Read more ...

    How to Fix Internet Explorer Cannot Download FileName from WebServer

    Tuesday, January 19, 2010
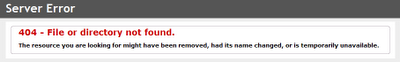
    You may find that when you create a link to a file from your web server that Internet Explorer cannot download or open the file.  When the user clicks the link, Internet Explorer returns the generic 404 error, as shown:

    They also may receive an error stating, "Internet Explorer cannot download filename.ext from www.server.com.  Internet Explorer was not able to open this Internet site.  The requested site is either unavailable or cannot be found. Please try again later."

    This happens when IIS doesn't understand the file extension and associated content type of the file.  Examples of such file extensions are .reg or .gadget.  To fix this problem you must add the extension and MIME type to IIS.

    Here's how you do it in IIS 7.0 (Windows Server 2008) and IIS 7.5 (Windows Server 2008 R2):
    • Open Internet Information Services (IIS) Manager
    • Expand servername > Sites > Default Web Site
    • Select the website you want to configure, or select Default Web Site if you want to configure all websites on the server
    • Double-click MIME Types in the IIS section of the center pane
    • Click Add in the Actions pane
    • Enter the extension you wish to add, including the . prefix (i.e., .reg or .gadget)
    • Enter the MIME type (i.e., text/plain for .reg files or application/x-windows-gadget for .gadget files)
    • Click OK
    The changes go into effect immediately - there's no need to restart IIS.

    For a quick reference of MIME types, see MIME Type Detection in Internet Explorer.
    Read more ...

    How to Enable Reverse DNS Lookup in IIS

    Tuesday, January 5, 2010

    This article explains how to enable reverse Domain Name System (DNS) lookup for all versions of Internet Information Services (IIS).

    When reverse DNS lookups are enabled on the web server, the IP address of each web client that connects to the IIS server is resolved to a DNS name, and the DNS name instead of the web client IP address is placed in the IIS log files.  Enabling reverse DNS also affects what CGI and ISAPI extensions see as a value of the Remote_Host variable.

    Microsoft KB article 297795 gives a step-by-step demonstration how to enable RDNS for IIS4, IIS5 and IIS6, but all you need to do is run the following in a command prompt from the ADScripts folder:

    For IIS4 run:
    adsutil set w3svc/EnableReverseDNS TRUE
    For IIS5 and IIS6 run:
    cscript adsutil.vbs set /wesvc/EnableReverseDNS "TRUE"
    In IIS7, you must install the IP and Domain Restrictions role service for the Web Server (IIS) role.  You can do this in Server Manager or from the command line using the following command:
    ServerManagerCMD -install Web-IP-Security
    In Windows Server 2008 R2, the ServerManagerCMD.exe program is deprecated and has been replaced with the ServerManager Powershell cmdlets.  The following two cmdlets are used to install the IP and Domain Restrictions role service:
    Import-Module ServerManager
    Add-WindowsFeature Web-IP-Security
    Now that the role service is installed, you can configure reverse DNS lookups, as follows:
    • Open Internet Information Services (IIS) Manager.
    • Navigate to the Server Name in the Connections pane.  If you only want to enable reverse lookups on a particular website, navigate to that website.
    • Double-click IP Address and Domain Restrictions in the center pane and click Edit Feature Settings in the Actions pane.
    • Put a checkmark in Enable domain name restrictions and click OK.
    You will see the following warning:
    Restricting access by domain name requires a DNS reverse lookup on each connection. This is a very expensive operation and will dramatically affect server performance. Are you sure you want to enable restrictions based on domains?
    Clicking Yes will enable reverse lookups for all clients connecting to the web server.  I have not noticed any more than a 1-2% increase in CPU performance and the websites are just as performant as before.

    Each of these changes go into effect immediately.  There is no need to restart IIS.
    Read more ...

    Configuring Virtual Directories with Directory Browsing in IIS7

    Thursday, March 20, 2008

    A website that uses directory browsing is a convenient way to display the files and folders in a directory using a web browser. An example of this is demonstrated here.

    To configure directory browsing in IIS6, you simply enable the Directory Browsing checkbox on Home Directory tab of the virtual directory. If you want to configure it so that users are required to authenticate to access the virtual directory, you disable anonymous access, enable Basic Authentication and configure the appropriate NTFS permissions on the target folder.

    It's slightly different in IIS7 since IIS7 introduces the concept of delegated administration. This means that you can have the IIS configuration in web.config files which reside in the virtual directory. IIS has to read these config files very early in the connection attempt, i.e. when there is no authenticated user available yet. For this reason IIS has to use the process identity (usually Network Service) to read the web.config file.

    To configure a virtual directory for directory browsing in IIS7:

    • Create or select the virtual directory in Internet Information Services (IIS) Manager
    • Double-click Authentication and select the appropriate authentication methods for the Vdir (default is Anonymous)
    • Select the Vdir again and double-click Directory Browsing. Click the Enable action
    • Right-click the Vdir and select Edit Permissions. Configure the NTFS permissions for the target folder and ensure that Network Service has read access to the folder

    If you don't grant the Network Service account read rights on the Vdir, you'll get the following error when accessing it:

    500 - Internal server error.

    There is a problem with the resource you are looking for, and it cannot be displayed.

    Read more ...

    Automatically Reset the FTP Service in Windows Server 2008

    Monday, March 3, 2008

    One of the more popular tips I've posted is, "How to automatically reset the FTP service," in Windows Server 2003. This tip is useful for public FTP sites where bad guys are trying to hack in, usually using a dictionary attack.

    Doing the same thing in Windows Server 2008 is slightly different and has an important caveat - It will not work with the Microsoft FTP Publishing Service for IIS 7.0 yet. It will work fine if you use the standard FTP Publishing Service, included on the Windows Server 2008 DVD.

    As in my original post, create a batch file named C:\Scripts\ResetFTPService.bat, as follows:
    net stop msftpsvc
    ping -n 10 127.0.0.1
    net start msftpsvc
    The batch file stops the FTP service, pings the loopback adapter 10 times to create a 10 second pause, and starts the FTP service again. Stopping the FTP service causes the hacker's session to be dropped immediately. Since no one can connect for 10 seconds, this creates a form of "tarpitting", making it too expensive to continue the attack.

    To make the script run automatically on the correct event, use the Windows Server 2008 Task Manager:

    • Right-click Task Manager (under Configuration in Server Manager) and select Create a Basic Task

    • Name the task, "Reset FTP Service" and click Next

    • Choose When a specific event is logged as the Task Trigger, click Next

    • Select Log: System, Source: IIS-FTP, and Event ID: 100. Click Next

    • Select Start a program and click Next

    • Enter C:\Scripts\ResetFTPService.bat for the Program/script and click Next

    • Click the checkbox for Open the Properties dialog for this task when I click Finish and then click Finish

    • In the Properties window select Run whether user is logged on or not and Run with highest privileges

    • Click OK

    • Enter the User name and Password for running this task

    This causes the ResetFTPService.bat batch file to run whenever an event ID 100 with source IIS-FTP is logged in the System event log.

    Remember, this will not work with the Microsoft FTP Publishing Service for IIS 7.0 because this service strangely does not log failed logon attempts to the event log. I've posted a request to the IIS7 team for this functionality.

    Read more ...

    EXPTA Server Upgrade

    Monday, January 21, 2008
    I ordered a new server this weekend to replace my existing Windows Server 2003 infrastructure. This new server will run the same roles as my existing server, but will have twice as much RAM and will be "green." It will utilize the new AMD Athlon X2 BE-2400 Brisbane 2.3GHz 45W Dual-Core CPU, less cooling (due to the low wattage CPU), and a smaller power supply. Should be fun. I haven't built my own hardware since the 90's. :)

    I'll be building it with x64 Windows Server 2008 Enterprise edition and utilize Hyper-V for my virtual DC and Exchange 2007 servers, instead of VMware. The host server will function as my Exchange 2007 Edge server and host the www.expta.com blog on IIS 7.

    The plan is to bring up the the new W2K8 server, build new virtual DC and Exchange servers, move the mailboxes to the new Exchange server, install the Exchange Edge role, and move the blog to the new server. Once I know everything is working properly I'll decommission the old Windows 2003 and Exchange 2007 servers.

    Hopefully, there will be very little downtime. I only expect brief outages as I update my router configuration. As usual I'll post my experiences with the upgrade, as will as any troubleshooting tips and gotchas I discover along the way.

    Read more ...

    Installing or switching ASP.NET versions on x64 platforms

    Monday, November 5, 2007
    When installing SQL 2005 on an x64 server, I came across the following warning:


    32-bit ASP.Net is Registered. Required 64-bit ASP.Net to install Microsoft Reporting Services 2005(64-bit).
    This article explains how to install and enable the correct version of ASP.NET for x64 platforms to fix this error.

    After you install the ASP.NET redistributable packages, you can switch between the different versions of ASP.NET. To do this, follow these steps for each ASP.NET version:


    ASP.NET 1.1, 32-bit version
    To run the 32-bit version of ASP.NET 1.1, follow these steps:
    1. Click Start, click Run, type cmd, and then click OK.
    2. Type the following command to enable the 32-bit mode:


    cscript %SYSTEMDRIVE%\inetpub\adminscripts\adsutil.vbs SET W3SVC/AppPools/Enable32bitAppOnWin64 1
    3. Type the following command to install the version of ASP.NET 1.1 and to install the script maps at the IIS root and under:


    %SYSTEMROOT%\Microsoft.NET\Framework\v1.1.4322\aspnet_regiis.exe -i
    4. Make sure that the status of ASP.NET version 1.1.4322 is set to Allowed in the Web service extension list in Internet Information Services Manager.


    ASP.NET 2.0, 32-bit version
    To run the 32-bit version of ASP.NET 2.0, follow these steps:

    1. Click Start, click Run, type cmd, and then click OK.
    2. Type the following command to enable the 32-bit mode:


    cscript %SYSTEMDRIVE%\inetpub\adminscripts\adsutil.vbs SET W3SVC/AppPools/Enable32bitAppOnWin64 1
    3. Type the following command to install the version of ASP.NET 2.0 (32-bit) and to install the script maps at the IIS root and under:


    %SYSTEMROOT%\Microsoft.NET\Framework\v2.0.50727\aspnet_regiis.exe -i
    4. Make sure that the status of ASP.NET version 2.0.50727 (32-bit) is set to Allowed in the Web service extension list in Internet Information Services Manager.


    ASP.NET 2.0, 64-bit version
    To run the 64-bit version of ASP.NET 2.0, follow these steps:

    1. Click Start, click Run, type cmd, and then click OK.
    2. Type the following command to disable the 32-bit mode:


    cscript %SYSTEMDRIVE%\inetpub\adminscripts\adsutil.vbs SET W3SVC/AppPools/Enable32bitAppOnWin64 0
    3. Type the following command to install the version of ASP.NET 2.0 and to install the script maps at the IIS root and under:


    %SYSTEMROOT%\Microsoft.NET\Framework64\v2.0.50727\aspnet_regiis.exe -i
    4. Make sure that the status of ASP.NET version 2.0.50727 is set to Allowed in the Web service extension list in Internet Information Services Manager.


    ASP.NET on Windows Server 2008
    The bits for the correct platform of ASP.NET on Windows Server 2008 are included in the OS cache. To install ASP.NET on Windows Server 2008 (x86 or x64) follow these steps:

    1. Run Server Manager
    2. Select Roles and click Add Roles
    3. Select Web Server (IIS). Click Add Required Features if prompted
    4. Select ASP.NET in Role Services and run through the rest of the wizard to complete the installation

    If the Web Server (IIS) role has already been installed on your server, do the following to add ASP.NET:

    1. Run Server Manager
    2. Expand Roles and select Web Server (IIS)
    3. Click Add Role Services in the right-hand pane
    4. Add the ASP.NET role service and run through the wizard to complete the installation

    Read more ...